Why don't we just block the fraudster's IP address and be done with it?
Why an IP address rarely identifies just one person: IPv4, IPv6, NAT, shared networks, VPNs and the limits of IP blocking and geolocation in fraud detection.
 By Ivan Skula
July 6, 2023
One common fraud-mitigation practice I have observed is leveraging IP addresses. This could be blocking transactions linked to high-risk countries or mitigating an attack from a particular IP address. Unfortunately, not every use case I saw considered IP address limitations. To use IP addresses to the fullest, you need a certain level of technical networking knowledge.
IP address
There are two different versions of IP protocols - IPv4 and IPv6 (there was also IPv5, which is considered experimental). IPv4 has been around since the early 1980s, is the most commonly used protocol, and is a foundational part of today's internet. IPv4 is connectionless, which means that when two devices want to communicate via IP, they don't need to establish a connection or session (unlike TCP). Each of these two devices must still be assigned a unique IP address. When we refer to an IP address in our discussion, we usually mean an IPv4 address.
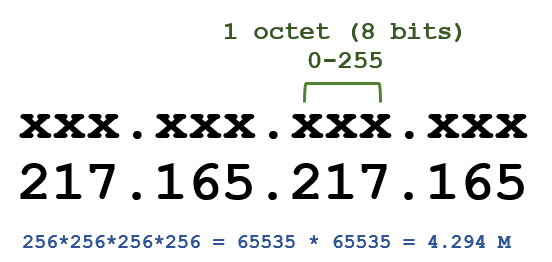
An IPv4 address is a 32-bit number commonly represented in dotted notation, separating 4 numeric values ranging from 0 to 255 (an octet). All addressable IP addresses therefore technically range from 0.0.0.0 to 255.255.255.255. IP address [217.165.217.165] can be written in multiple ways - replacing the decimal octets with hexadecimal (d9.a5.d9.a5) or as an integer number without dots (3651525029).
Mathematically, IPv4 can address ≈4.3 billion devices in the network. In practice, certain ranges are allocated for specific purposes. Below are the most common ones you might have encountered. The loopback range, from which we commonly use the address 127.0.0.1, represents localhost or the machine we are actually sitting behind. Three other ranges are also commonly known (especially the last one, 192.168.xxx.xxx). We often use them when we configure our local home networks. A few more, like multicast or reserved addresses, reduce the number of addressable IPs to less than 4.3B.
Loopback range:
- 127.0.0.0 - 127.255.255.255
Private ranges:
- 10.0.0.0 – 10.255.255.255
- 172.16.0.0 – 172.31.255.255
- 192.168.0.0 – 192.168.255.255
Though the number 4.3B might feel like quite a lot, when you ask Google how many computers there are, it will come up with a number ≈2B in 2019, including laptops and servers. But don't forget that one server can have multiple network cards and connections, and the same applies to a common laptop, which usually has one Ethernet and one Wi-Fi Network Interface Controller (NIC).
The number of mobile phones is much bigger. There were ≈15B devices in 2021. Even if we agree that not all of them are connected to the internet, it's clear that IPv4, with its 4.3B addresses, is simply not enough. And though those numbers are high, we also have to consider the Internet of Things (web cameras, Alexas, smart appliances, etc.) as well as Industrial IoT.
So what magic lets us still use IPv4 with so many devices connected to the internet? There were multiple technologies developed and deployed, but 2 of them link to our topics (we are still trying to stay in the fraud prevention domain):
- Network Address Translation (NAT)
- IPv6
If you are familiar with them or want to skip the details about NAT and IPv6, you can skip the section starting with Extra: and continue reading below!
Extra: Network Address Translation (NAT)
If 4.3B devices is a limit for a network of interconnected devices in IPv4, what if we could separate the devices into separate addressable networks? Imagine my home network uses the above-mentioned range 192.168.xxx.xxx, and your home network uses the same range, while all your home devices have unique addresses within your network. In simple terms, NAT lets us do this.
Suppose a computer or phone on your home network needs to communicate with another computer on the internet. In that case, your router will apply an address translation - replacing your local network IP source address with its assigned IP while remembering your device request (using ports), so it can forward the communication from the remote machine back to your laptop or phone specifically once the response packets arrive to the router.
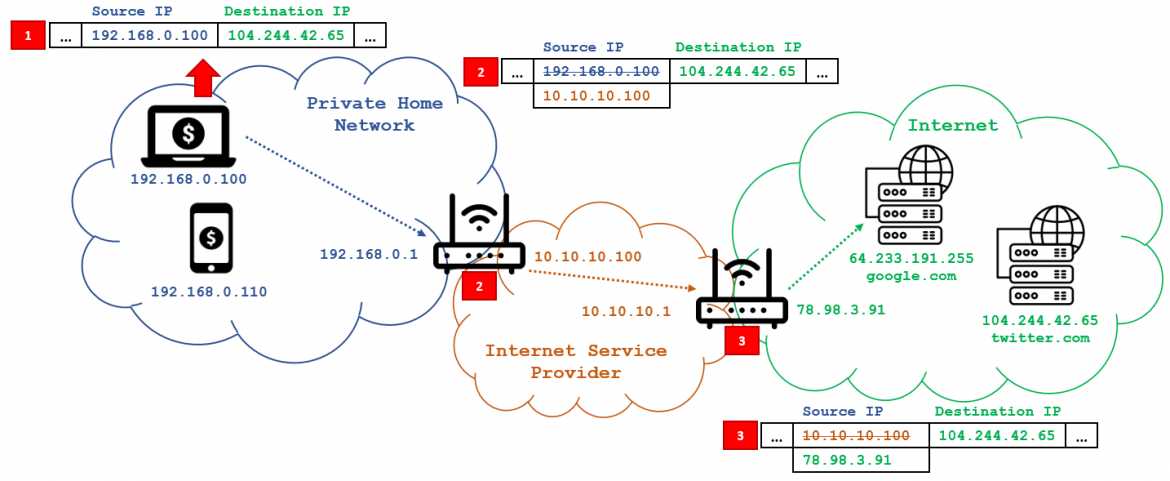
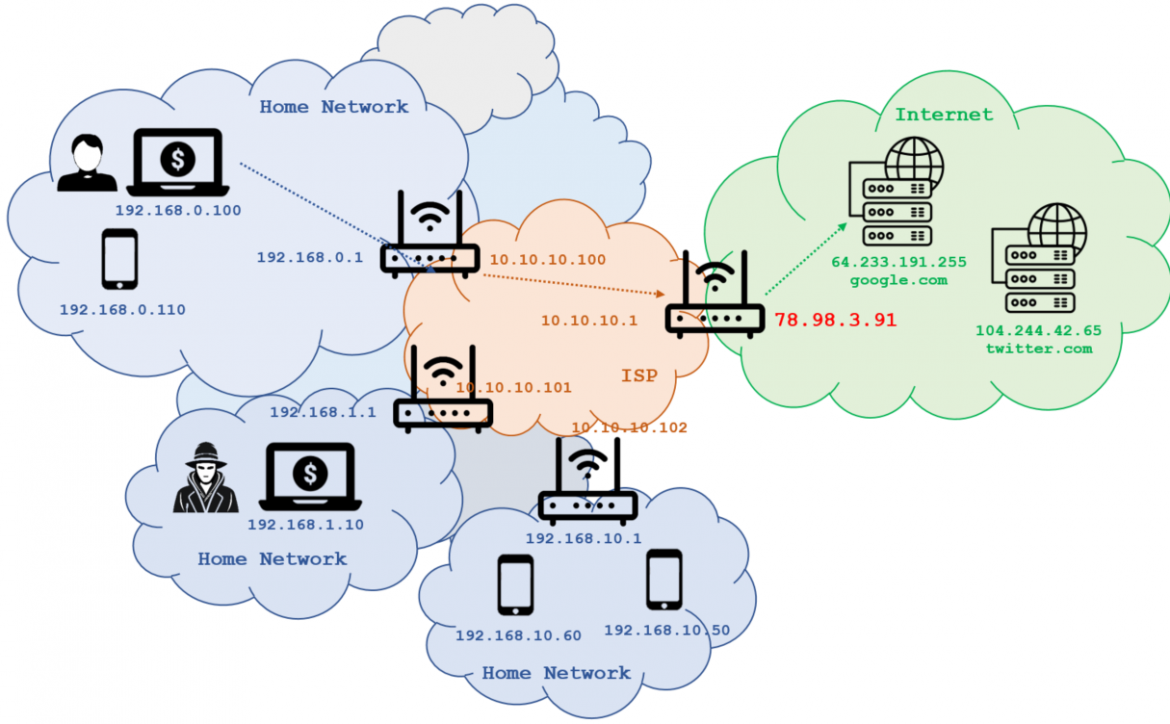
The diagram above shows a laptop with local IP 192.168.0.100 trying to access the twitter.com server at IP address 104.244.42.65. So the packets traverse from the laptop to the local private home network router, where the first translation happens. Then, the second translation happens between the Internet Service Provider (ISP) internal network and the Internet. We can also see that the ISP uses IP address 78.98.3.91, which is unique globally, and this address is one of the addresses from our original 4.3B bucket of IPv4 addresses.
Thanks to NAT, many more devices can connect to the internet than the available range of IPv4 addresses. NAT was created and deployed in 1993, and a few years later, in 1998, IPv6 was released.
Extra: IPv6
IPv6 was supposed to resolve the issues linked to the insufficient address space, while NAT and CIDR were supposed to extend the adoption period from IPv4 to IPv6.
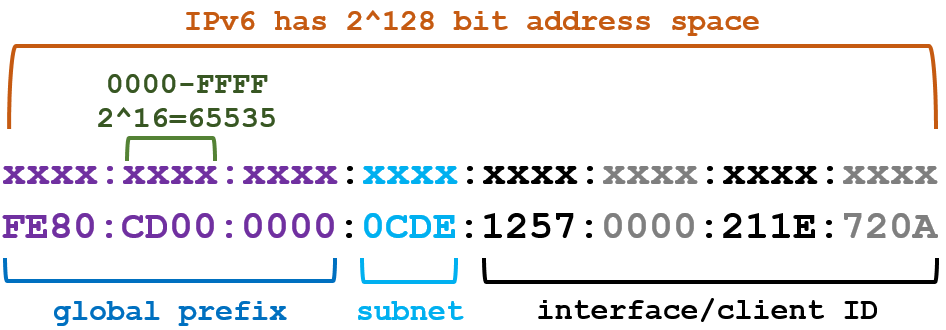
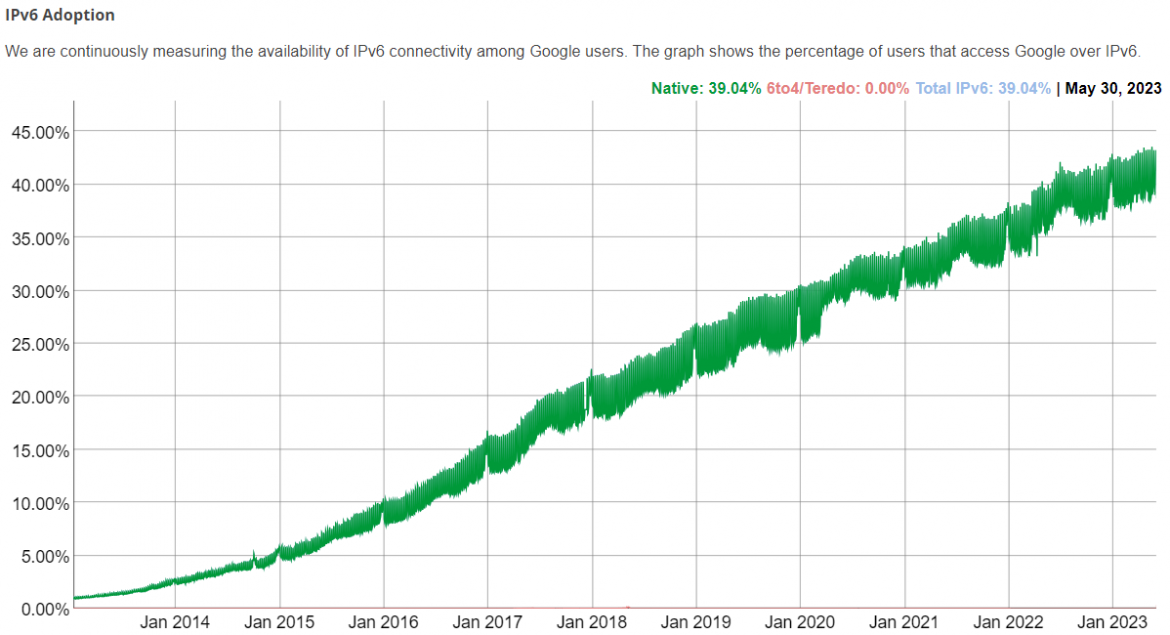
IPv6 has 2^128 addresses, which in simplified terms gives (as per Google) 5*10^28 to every one of approx 6.5B humans on Earth, or 2^52 addresses for every observable star in the known universe :) So it is really a lot. Like IPv4, IPv6 has special ranges dedicated to various use cases. Also, there is (obviously) no need for NAT anymore, as every device can have its own unique IP.
Despite IPv6's many benefits, its adoption is much slower than anticipated. IPv6 hosts cannot communicate directly with IPv4 hosts and must use special gateway services. Also, switching from IPv4 to IPv6 at an organizational level requires significant technical expertise and effort.
IP address - to block or not?
Now, steering back a bit to fraud prevention, to break down what blocking an IP address means, I will use a diagram. When a customer connects from his Laptop to the internet [IP: 192.168.0.100], Google or Twitter will not receive the actual IP of the laptop assigned within the home network but will receive only the assigned global IP of the Internet Service Provider [red highlighted IP 78.98.3.91]. The same will be true for a fraudster [IP:192.168.1.10] who uses the same ISP. Google or Twitter will see him with the same IP [red highlighted IP 78.98.3.91]. Of course, if criminal activity happens, police can ask the ISP to identify the actual customer who connected to Google or Twitter at a given time, but police handle this as part of the criminal investigation.
So can we, or should we use IP blocking? I would break it down to 2 different use cases.
- If your customers are almost entirely located in your country of operations, you can block IPs assigned outside your country with little impact. This also applies if you service several countries but not others.
- If your customers are or can connect from anywhere, be aware that you are not blocking one particular customer or device; you are probably blocking an endpoint through which you might also be blocking good customers.
Be extra cautious when blocking IPs assigned within your country of operations. In this case, I'd use the IP-blocking rule only as a temporary solution for fraud you need to stop immediately, when you have nothing more granular than the IP the attack is coming from. Replace this rule ASAP with a focused one that targets a more specific pattern than just an IP address (e.g., customer behavior, tnx. amounts, or velocity).
IP address - can I use it for geo-location?
So far, we have talked a lot about the technical side of IP addresses and how there aren't enough addresses for everyone. But one crucial aspect of IP in fraud detection is linking the IP address to a particular geography.
I was lucky enough to find a secret mapping of how through IPv4 as well as through IPv6, your geo-location can be revealed - see below.
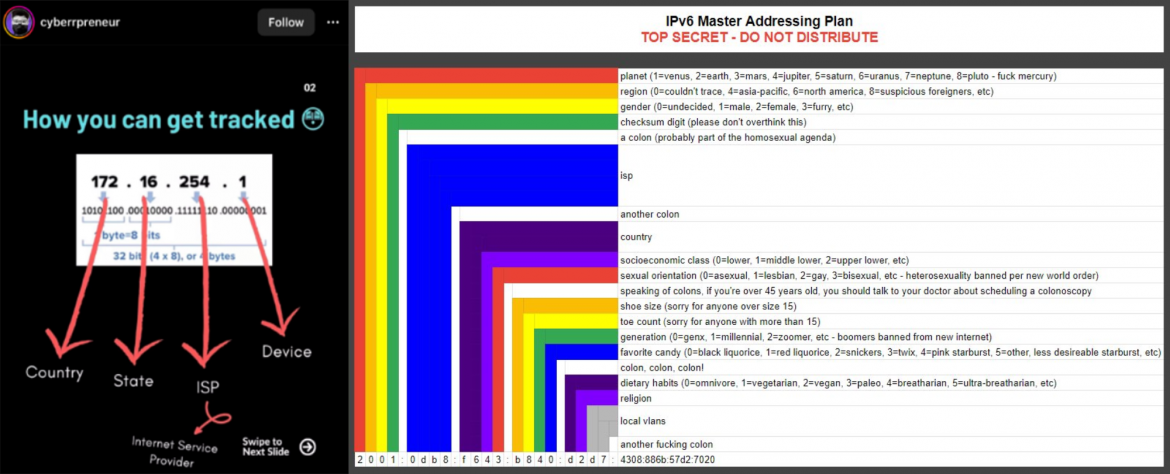
OK, ok, jokes aside. The above is complete nonsense, but it is a fact that IPv4 can be translated into geo-location, as all IPv4 addresses are allocated by the Internet Assigned Numbers Authority (IANA), a department of the Internet Corporation for Assigned Names and Numbers (ICANN).
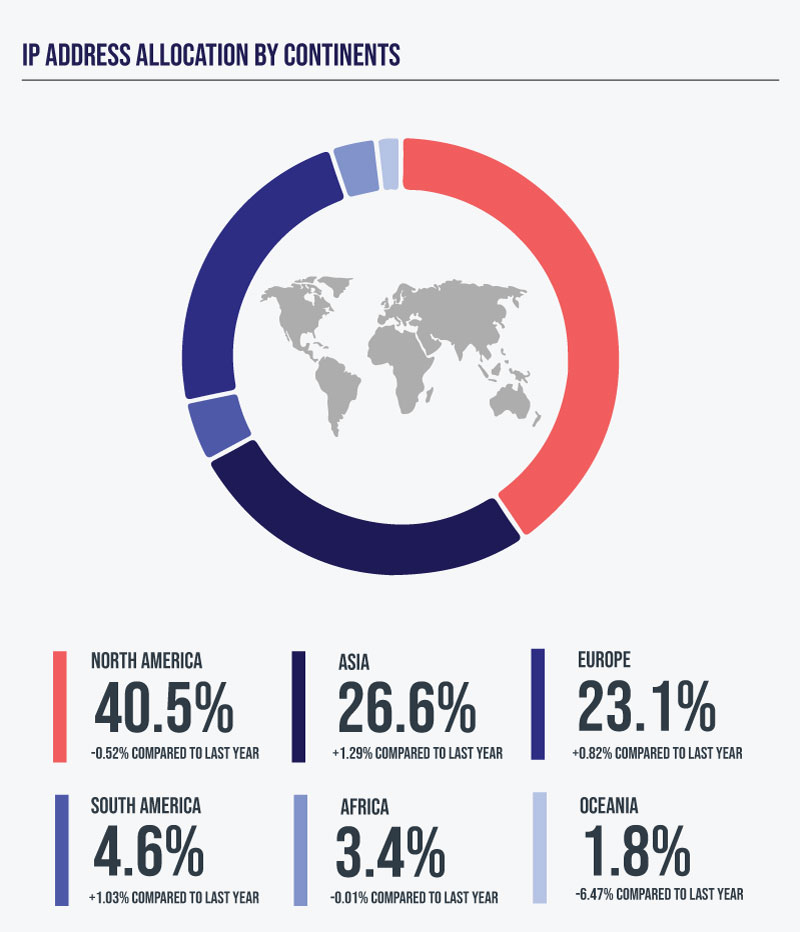
Historically, IPv4 address allocations have been highly imbalanced in favor of the US 1. Still, IANA assigns address ranges (lately based on their demand) from those available ones to Regional Internet Registries (RIRs), those are further cascaded to National Internet Registries (NIR) and those allocate them further to Local Internet Registries (LIR) or Internet Service Providers (ISPs) who can use them or rent them further to their customers - companies or even individuals.
For example, UAE has been provided with 2,838,400 IPv4 addresses, the Kingdom of Saudi Arabia with 5,504,256, and my home country - Slovakia with 2,555,392 2.
From the above, you can already see that each allocated IP is assigned to a specific country via NIR and then further down to LIR or ISP, which will have multiple endpoints throughout a given country with allocated global IP addresses. Therefore, the geolocation for a given IP address can be as granular as the city or ZIP level.
Now, stating the above, we can't forget to highlight that there are ways to alter the IP address of the device we are connecting from - via VPN or Proxy servers. Fraudsters can use VPNs and proxy servers to mislead or confuse the counterparty. But VPNs can be used for legitimate purposes as well - for example, to bypass geo-based filters where certain web services are only provided to specific geographies - e.g., US content on Netflix is much broader than in other regions, so you might want to use a VPN to gain access to US content.
In our case - fraud prevention - fraudsters, especially the tech-savvy ones, will undoubtedly use VPN not only to hide their actual ISP's IP but also to complicate back-tracking of their digital footprint by connecting via countries with favorable legislation or countries with limited capacity to investigate cybercrime.
To cite an example from a Sift report: "The attack demonstrated how cybercriminals have remodeled typical ATO techniques to make a greater impact: using bots, proxy servers, and millions of compromised credentials, they were able to cycle through millions of usernames and passwords, while simultaneously and rapidly switching IP addresses in order to hide the origin of the attacks—and avoid getting blocked by typical rules-based fraud prevention systems. In fact, the largest group—or cluster—of blocked IP addresses grew by 50x between Q1 and Q2 2021." 3
Europol in its IOCTA 2023 report states, "Virtual Private Networks (VPNs) are the most common services cybercriminals use to shield communication and Internet browsing by masking identities, locations, and the infrastructure of their operations."4
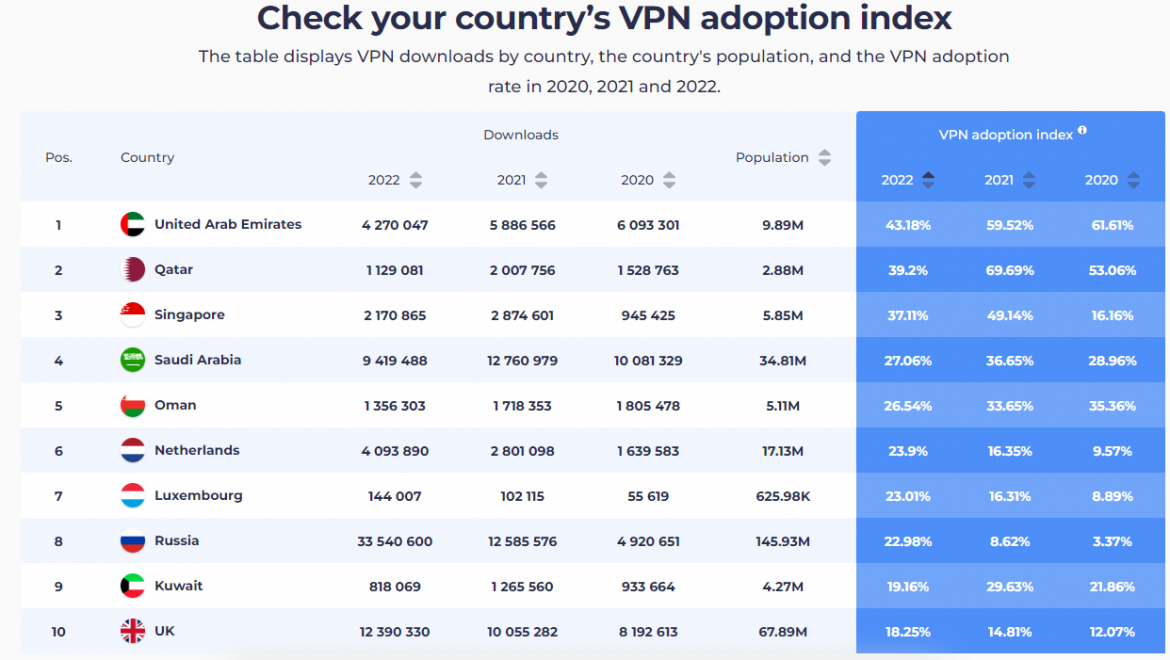
Geo-location-based rules derived from IP may also trigger many false positives when VPN or proxy use is common among the general public. Some countries with the highest VPN usage are listed above, and GCC countries are among them 5.
So utilize geolocation based on IP address with caution and make sure it fits your particular use case, considering the fact that IP addresses can and often are altered.
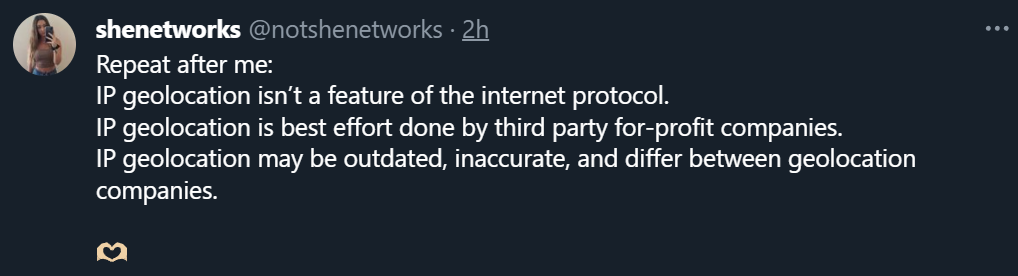
The post below highlights the most important aspects of IP geolocation:
References & Further Reading
[1] IPv4 Address 2022 Infographics
Historical infographic showing how IPv4 address allocations were distributed by country and continent in 2022.
[2] IP Address by Country 2026
Living country table; the current edition is not an archived record of the figures quoted in this 2023 article.
[3] Q3 2021 Digital Trust & Safety Index: Account Takeover
Sift research on account-takeover attacks, including the use of bots, compromised credentials and rotating IP addresses.
[4] Internet Organised Crime Threat Assessment (IOCTA) 2023
Europol assessment of organised cybercrime, including services used to conceal identities, infrastructure and communications.
Historical VPN-adoption comparison.
Continuously updated measurements; the article reproduces a historical view.