Changing face of phishing or what to be aware of!
How phishing evolved from mass email into targeted messages, voice impersonation, misleading domains and AI-generated QR codes, and why awareness remains important.
 By Ivan Skula
June 9, 2023
From mass emails to targeted attacks
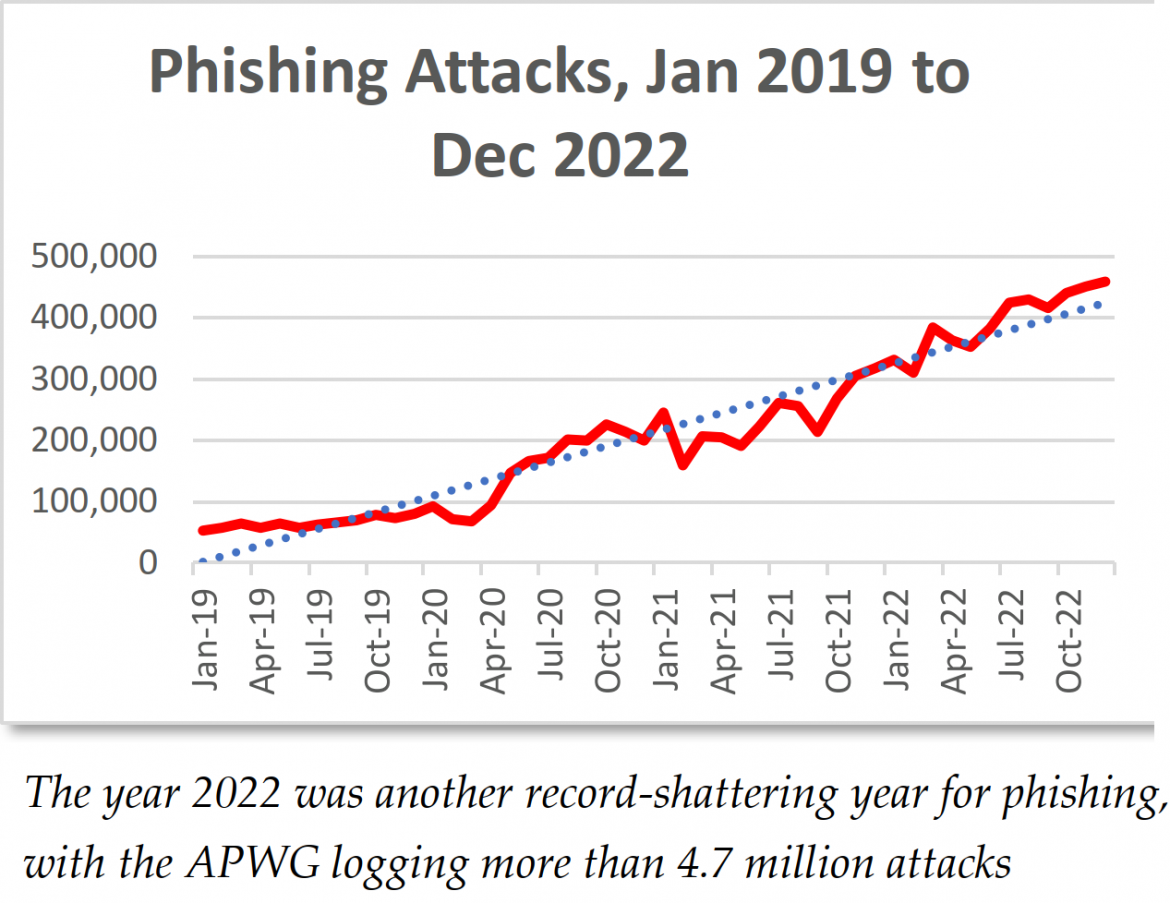
Phishing is one of the oldest techniques of cybercrime - it actually showed up first in 1995. Every day, millions of people are targeted by phishing attacks. Phishing losses run into the billions of US dollars, and despite its age, its ever-evolving nature means its impact grows year over year1.
While in 2006 we recorded 100K phishing domains in one year for the first time, in August 2020 we recorded the same number of new phishing domains in just one month.
In the early days, phishing attacks were mainly deployed in the so-called "spray and pray" fashion, where the attacker generates thousands of identical e-mail messages, distributes them to potential victims, and waits for those who will fall prey to his lure. The initial primary attack vector was email because it costs almost nothing to automate and generate thousands of these emails as needed.
While these techniques are still widely used today, more advanced techniques have emerged (big thanks to social networks, where people publicly share many details from their lives). These include customized attacks targeting a group (spear-phishing, for example, aimed at employees in the finance dept.) or even a single person (whaling, e.g., targeting C-level executives or upper managers). In these messages, attackers adjust and personalize content to improve perceived authenticity and increase the chance of success. Publicly available information helps the attacker gather relevant knowledge about a potential victim; one example of this attack is the well-known Business Email Compromise (BEC).
BEC caused the highest losses across all categories2. BEC showed up first-time in the FBI IC3 report from 2014 with the attributed loss of $60M against ≈1500 victims; a year later, in 2015, the number of victims rose to ≈8000, and the losses ≈250M USD. In 2018, losses passed the 1B USD mark, reaching ≈1.3B USD, with ≈20K victims. Since then, the number of victims has stayed around 20K, but the amount keeps growing. In 2019, losses were ≈1.8B USD; in 2020, ≈1.9B USD; in 2021, ≈2.4B USD; and in 2022, more than 2.7B USD. These are horrific numbers. Only last year has the investment scam taken the number one spot from BEC, which held this position since 2015.
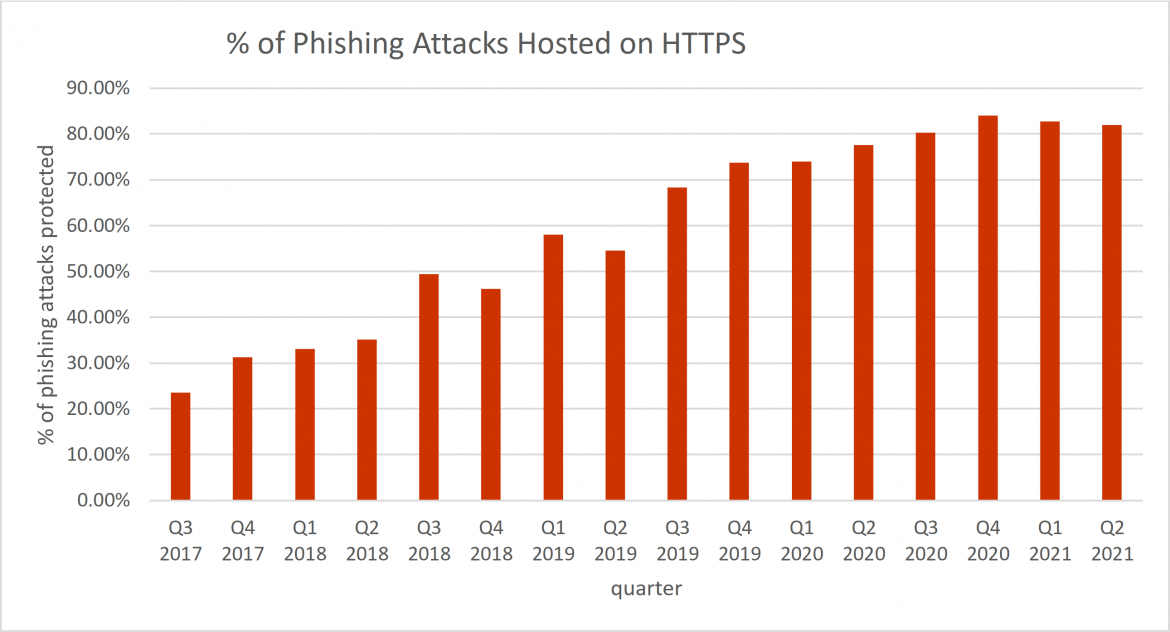
One early adjustment that helped phishing websites appear genuine was the use of HTTPS. This showed a small padlock in the address bar, which misled visitors into believing the page was secure and authentic; unfortunately, it still works on potential victims today. That's also a reason why, since 2020, more than 80% of phishing sites use HTTPS3.
Beyond email: voice, SMS and social networks
In the last few years, we have also seen an increased use of other e-channels than email for phishing attacks - more specifically, voice or SMS. Voice phishing (vishing) and SMS phishing (smishing) date back to 2004. Voice phishing has gradually caused losses of more than 800M USD, according to last year's FBI IC3 report, with the majority (almost 600M USD) linked to elderly (>60 years) victims2.
Another future problem linked to vishing is the use of generative AI to mimic the voice of any selected individual whose voice sample can be obtained. In the media, there are already instances of vishing where the victim believed that he or she was speaking with a family member in distress4.
Phishing naturally moved beyond email and SMS to other communication platforms - some connected to social networks like Facebook Messenger, others as standalone apps like Telegram, WhatsApp, and others. One of the most common types of attack perpetrated via social networks is the Confidence/Romance scam, which amounted to more than 700M USD in 2022 and impacted almost 20K victims2.
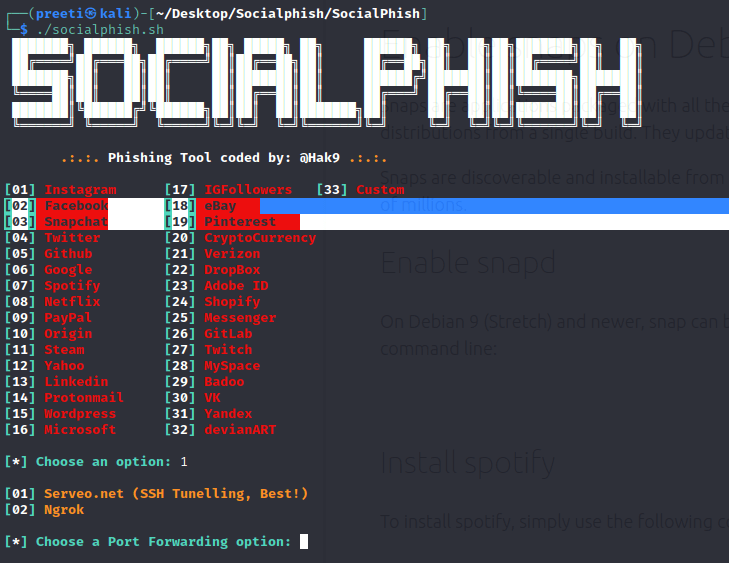
Although mimicking and spoofing e-commerce companies (eBay, PayPal, etc.) began in 2003, tools like phishing kits now exist that can generate selected websites from templates (e.g., SocialPhish, ShellPhish, King-Phisher, Zphisher, and others).
Deceptive domains and disguised links
Websites have registered domains organized in a hierarchy, where the highest level visible to users is the Top-Level Domain (TLD). The most common TLD is [com]; you may also be familiar with other gTLDs like [net], [biz], and [org]. Since early May this year, Google released 8 new TLDs: [dad], [phd], [prof], [esq], [foo], [nexus], [zip], and [mov]. 5 Especially the last two - [zip] and [mov] have been heavily criticized by the cybersecurity community, as they can be weaponized by cybercriminals for phishing. And they were pretty right, as the first instances of these new domains were detected as early as the 13th of May - [hxxp://microsoft-office.zip] followed in a few days by [hxxps://google-drive.zip], [hxxp://tax-return-2022.zip] and [hxxp://newdocument.zip]
Phishing attacks using phishing webpages deploy various techniques to hide or obfuscate the actual domain. These include using UNICODE characters that look like ASCII characters, using IP addresses instead of domain names, and typosquatting, where the attacker registers a very similar-looking domain to the one being imitated (e.g., amozon.com or microsofl.com). One amazing tool is URL shorteners (bit.ly, tinyurl.com, and many others), which hide the actual phishing domain behind an unreadable hash 6.
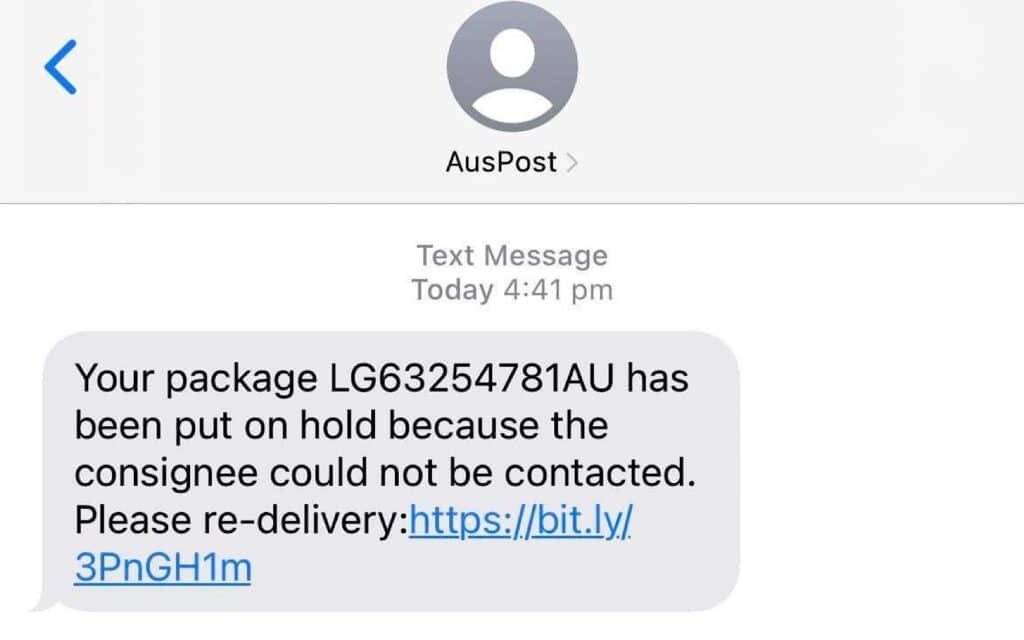
QR codes and AI-generated disguises
Last but not least, QR codes are another tool that helps hide the phishing domain. QR codes are a powerful weapon in the hands of cybercriminals running phishing attacks because they are unreadable to humans and, as such, extremely hard to spot or classify as suspicious. And recently - with a bit of help from generative AI - there are even amazingly looking QR codes, which will surely be used for phishing attacks789.
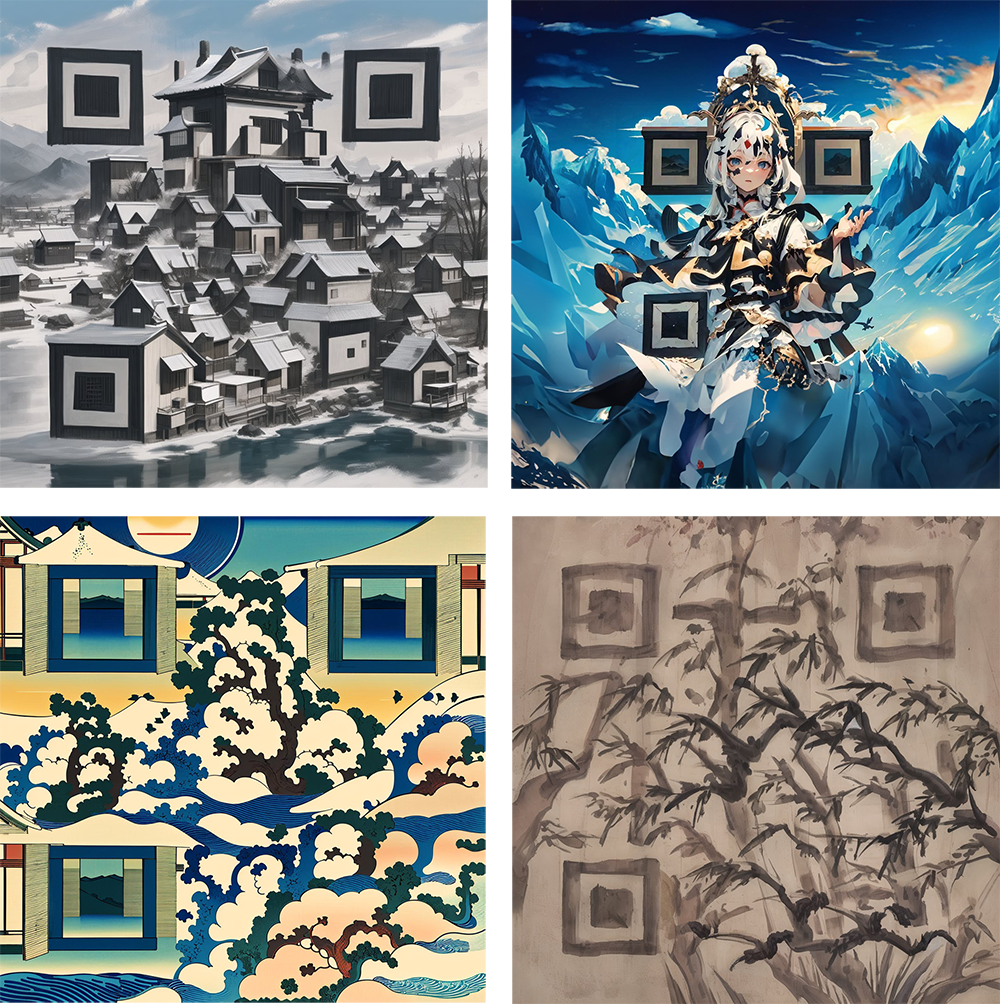
And here, our journey ends. The above is not an exhaustive list of changes and techniques used in phishing attacks. Phishing is truly a phenomenon about which books can be written. But I believe the points above showcase the versatility and effectiveness of various phishing techniques and their evolution over the years.
Given the number of phishing victims, I hope you never fall victim to phishing, and I ask you to spread awareness, as that is one of the core countermeasures in the fight against it.
References & Further Reading
[1] Phishing Activity Trends Report, 4th Quarter 2022
APWG's October-December 2022 report. Pages 2-4 cover reported phishing-site/attack growth and the 2019-2022 chart. Release date follows APWG's announcement; the PDF cover incorrectly prints 2022. These are reported phishing sites/attacks, not a count of all registered domains or total financial losses.
[2] 2022 Internet Crime Report
Official report: BEC discussion on page 10; tech/customer-support and government-impersonation fraud on page 16; complaint counts and losses on pages 21-24. The roughly $806.6 million total is Tech Support, not all voice phishing. Earlier annual BEC figures require the corresponding historical reports.
[3] Phishing Activity Trends Report, 2nd Quarter 2021
Page 9 is the source of the HTTPS chart spanning Q3 2017-Q2 2021. PhishLabs reports 82% in Q2 2021 following a late-2020 peak. The plotted data do not support a blanket above-80% claim for every quarter of 2020.
[4] They thought loved ones were calling for help. It was an AI scam.
Subscription access may be required.
[5] 8 new top-level domains for dads, grads and techies
Google's announcement of .dad, .phd, .prof, .esq, .foo, .zip, .mov and .nexus. Early access began May 3 and general availability May 10, 2023. Supports the launch details, not the later malicious-domain examples.
[6] New Tactic: Shortened LinkedIn URLs Are Now Used As Phish Hooks
Discusses abuse of LinkedIn's lnkd.in shortened URLs to conceal phishing destinations, citing Jeremy Fuchs at Avanan. This example supports the URL-shortening discussion, not every domain-obfuscation technique.
Creator's demonstration of artistic QR codes. The creator links the original Chinese WeChat article from this thread; that WeChat page could not be retrieved for metadata verification. The demonstration does not establish that these particular QR codes were used in phishing.
[8] QRBTF - AI QR Code Generator
Official AI and parametric QR-code generator. Its project history dates the first AI-generated QR-code demonstration to June 2023. This is a continuously updated tool, not a dated research publication or evidence of malicious use.
[9] AI-generated QR code art: Snowy Village
Descriptive title for the original QR-art social post. Account and date are corroborated by embedded copies of the post; the direct X/Twitter page was unavailable during review. Artistic examples are not evidence of a deployed phishing campaign.