Customer in Control: Reducing Fraud Risk by Allowing Customers to Manage Their Own Exposure.
Give customers control over their fraud exposure through optional restrictions on products, channels and transactions, complementing the bank's detection and authentication controls.
 By Ivan Skula
July 13, 2023
The shift from account takeover to payment scams
As per the recent NICE-Actimize report1, Account Takeover fraud (ATO) grew YoY between 2021 and 2022 by more than 35%, while at the same time, Authorized Push Payments (APP) overtook ATO (by share of the cumulative amount of attempted incidents) by 12% - APP 56% vs. ATO 44%.
This shift from ATO to APP is assumed to result from improved defenses around customer authentication (e.g., via device fingerprinting). Nevertheless, the problem remains, and shifting to APP makes it even harder for FIs to distinguish fraudulent transactions from genuine ones.
As if the above wasn't enough, the UK government has pledged to give the Payment Systems Regulator (PSR) authority to force FIs to reimburse victims of APP fraud23. The final version of the document is still being prepared, but some practical exceptions already appear in the available early versions. While this is not a widespread approach globally, other countries are expected to adopt it as fraud losses continue to rise.
As a result of such initiatives, FIs will have to adopt more advanced techniques to be able to detect fraud, such as:
- more granular behavioral profiles,
- multiple entities (accounts, cards, channels, devices, etc.),
- network-based techniques as well as
- machine learning (ML) algorithms focused on specific use cases (account takeover, mule accounts, bust-out fraud, card not present fraud, cheque fraud, etc.)
Giving customers control over their exposure
While all of the above is most likely on the table for relevant business stakeholders with a well-defined roadmap, one area is rarely considered but could substantially complement the steps above: allowing customers to manage their own risk exposure. This is the same concept used in cybersecurity, aiming to reduce exposure or attack surface.
Such a strategy usually entails various actions like
- temporary or permanent disabling of certain functions available to the user
- "hardening" of the devices (computers, servers, mobile) by removing functionality that is not generally used by users to perform their work but could be abused by an attacker
- restrict access to resources based on the users' group membership privileges
- etc.
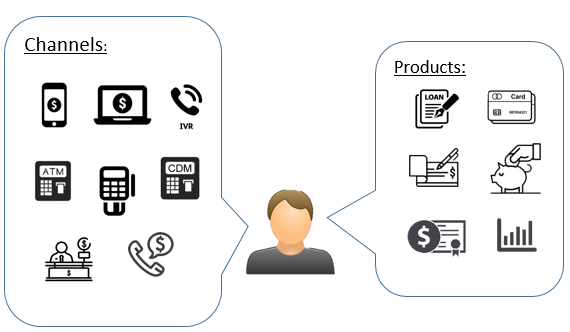
Like the above, FIs can implement functionality that lets customers manage or restrict the use of products, channels, or services.
For products, customers could temporarily block card use or disable the option to apply for a pre-approved loan.
For channels, customers could disable login to Internet banking from outside of the home country, or completely disable e-channels if the customer is elderly and only interacts with the bank through branches.
For services, customers could block on an ad-hoc basis:
- international transactions on cards,
- funds transfer above a certain amount,
- transactions against certain merchant types,
- funds transfer to unknown beneficiaries.
Another option is a "hardening" approach: add mandatory requirements for Step-Up authentication for customer-defined transactions (e.g., require MFA for CNP transactions by default).
Targeting the customers who benefit most
From the overall customer portfolio, only a small fraction of customers will likely be eager to adopt these functionalities. But we could leverage our marketing capabilities to target selected customers or segments (high net worth individuals, politically exposed persons, elderly, etc.) who might be priority targets or more susceptible to fraud.
Since FIs - as part of required fraud detection capabilities - are already doing entity profiling required for anomaly detection, this same data could be easily utilized for, e.g., generating a list of elderly customers owning a credit card that wasn't used outside of the country for the last 6 months, and we can promote an option (show them a message when they log in to Mobile Banking or Internet Banking) to temporarily disable international transactions to reduce their fraud risk exposure.
Many similar scenarios could significantly reduce customer fraud risk exposure. Another benefit of this approach is that we are giving the customers control over what services, products, and channels are enabled for them, so these restrictions will be:
- more accurate, as customers will enable them based on their future use expectations
- increased friction as a result of these restrictions will not damage the customer's perception of the bank, as it was they who enabled these restrictions
References & Further Reading
[1] 2023 NICE Actimize Fraud Insights Report
NICE Actimize report comparing fraud patterns and losses, used here for the discussion of account takeover and authorised payment scams.
[2] UK banks told to reimburse customers tricked by scams
Historical reporting on proposed UK reimbursement arrangements; not a statement of current rules.
[3] APP fraud reimbursement: What should your firm do next?
Historical explanation of UK authorised push-payment reimbursement proposals and preparation by financial institutions; not current legal guidance.